The Adams-Friendship Area School District in central Wisconsin is absorbing a vendor payment diversion that cost taxpayers more than $63,000 and ended with the business manager’s resignation. Reporting says a fraudulent third party inserted fake banking details into a legitimate $92,180 invoice thread with Cary Specialized Services for relocating modular classrooms — and that district Positive Pay and electronic funds transfer (EFT) policy safeguards were not followed.
WTMJ and WDEZ (citing WAOW-TV) describe a classic business email compromise (BEC) pattern: the bank rejected the first payment, finance pushed a second electronic payment after continuing the same email thread without out-of-band verification, and Cary Specialized Services reached out on August 19 after not being paid.
This is a dedicated News deep-dive — not a duplicate of the June 2026 Wisconsin school district listicle (which does not name Adams-Friendship). For a municipal parallel on coverage and lookalikes, see Surfside Beach’s $545K ACH loss.
We probed afasd.net (district site) and caryspec.com (reported vendor) on November 20, 2026 — website-tech, blacklist, and cybersquat scans below, plus public DNS for mail authentication.
Snapshot
| Field | Detail |
|---|---|
| Victim | Adams-Friendship Area School District (Adams County, WI) |
| Intended payee | Cary Specialized Services — $92,180 invoice to move relocatable classrooms from Illinois to the high school |
| Fraud type | BEC / vendor payment diversion (fake banking details in-thread) |
| First electronic payment | July 27, 2026 — bank flagged and returned |
| Second electronic payment | August 3, 2026 — different fraudulent banking details tied to Sendo Group LLC — cleared |
| Discovery | August 19, 2026 — Cary reported non-payment |
| Unrecovered loss | $63,128.53 expected remaining (WDEZ) · about $63,000 still lost (WTMJ) |
| Recovery | About $29,000 total recovered (WTMJ) — $25,000 cyber insurance (WTMJ) · $4,051.47 bank (WDEZ) |
| Crime insurance | Denied — employees did not independently verify banking info (WTMJ / WDEZ) |
| Controls skipped | EFT policy · Positive Pay (superintendent, WTMJ) |
| Staff outcome | Business manager suspended, then resigned |
| LE | Adams Police Department · tech staff and legal counsel consulted |
Timeline
| Date | Event |
|---|---|
| Before July 27 | Business manager emails Cary for electronic payment instructions; fraudulent party replies in-thread with fake bank details |
| July 27, 2026 | District submits payment #1 — bank rejects / returns it |
| Aug 3, 2026 | District submits payment #2 using new fraudulent account information (Sendo Group LLC attribution per WDEZ) — succeeds |
| Aug 19, 2026 | Cary Specialized Services contacts district — no payment received; fraud discovered |
| Nov 18, 2026 | WTMJ / WDEZ publish updates; insurance denial and staff resignation public |
What reporting says happened
WDEZ (Nov 18, 2026, citing WSAU-WAOW) adds process detail WTMJ compresses:
- The invoice itself was legitimate — transport of relocatable classrooms for the high school.
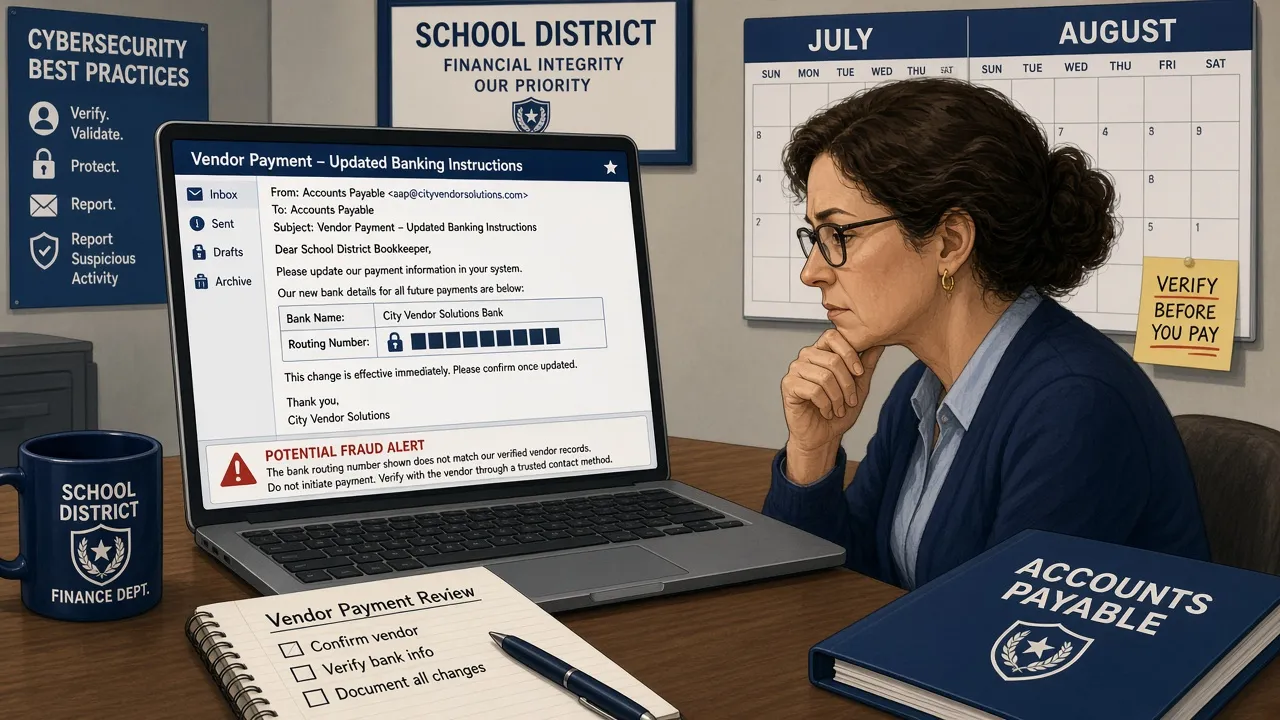
- When finance asked for EFT details, attackers who were not Cary supplied counterfeit routing and account data inside the same email conversation.
- After the July 27 return, staff did not restart verification on a known-good phone number or separate channel. They continued communicating in the same thread, then paid again on August 3.
- District leaders reported the matter to Adams Police, involved technology personnel, and consulted legal counsel.
- Cyber insurance recovered part of the exposure; the government crime insurance claim was denied for lack of independent verification of banking information (WTMJ / WDEZ).
WTMJ and WDEZ (Nov 18, 2026) report that the business manager was suspended, then resigned, and that the superintendent wrote financial safeguards — including an EFT policy and Positive Pay — existed but were not followed.
Public reporting does not name the email provider, whether the inbox was compromised, or whether a lookalike domain was involved. Treat domain posture below as parallel risk context, not proof of how this thread was hijacked.
Why K-12 finance teams should care
School districts run high-trust ACH seasons: construction, transport, food service, and specialist contractors. Wisconsin’s June 2026 district listicle is a separate statewide benchmark — it does not score Adams-Friendship.
BEC does not require malware on the bookkeeper’s laptop. It often wins when:
| Failure mode | Adams-Friendship reporting aligns? |
|---|---|
| Payment change accepted from email alone | Yes — fake bank data in-thread |
| First bank stop treated as noise, not incident | Yes — second attempt cleared |
| Positive Pay / EFT policy skipped | Yes — superintendent cites skipped controls |
| Insurance trigger = verified callback | Yes — crime claim denied |
Pair procedural controls with Google Workspace or Microsoft 365 hardening — but remember MFA on staff mailboxes does not stop a thief who only needs you to believe a forged banking-details reply.
What to do before the next vendor payment
- Out-of-band verify every new routing number — call the number on the W-9 / master vendor file, not the signature block in the email.
- Treat any returned ACH as a security incident until treasury confirms the beneficiary bank with Cary (or any payee) on a known-good line.
- Turn on Positive Pay (or equivalent) and make two-person review mandatory for first-time electronic payees.
- Enable Workspace / M365 phishing warnings (first-contact tips) on finance mailboxes.
- Tabletop “vendor says they were not paid” with superintendent, board, and insurer before the next construction cycle.
- Document which policy step failed — insurers and auditors will ask.
MFA: Google Workspace and Microsoft 365
afasd.net publishes Google Workspace MX (aspmx.l.google.com). Even when mail is on Google, district admins should enroll FIDO2 security keys and allow Google Authenticator-class TOTP for business managers and anyone who can move money.
| Grade | Meaning |
|---|---|
| Fail | SMS / email OTP only |
| Pass | Self-serve Google Authenticator-style TOTP |
| Strong | FIDO2 / YubiKey for sign-in |
| Platform | Grade | YubiKey | Authenticator |
|---|---|---|---|
| Google Workspace | Strong | Yes | Yes |
| Microsoft 365 | Strong | Yes | Yes |
Google Workspace admins can require 2-Step Verification with security keys and authenticator apps (Google Workspace admin — 2SV). Microsoft documents FIDO2 security keys and authenticator apps for Entra ID work accounts (Microsoft Learn — authentication methods). Grades follow our MFA directory.
Scope check: Strong MFA reduces mailbox takeover risk. It does not replace callback verification when a fake Cary reply arrives in an otherwise honest thread.
Recommended MFA tools
| Product | Best for | Get it |
|---|---|---|
| YubiKey 5C NFC | USB-C laptops + NFC phones | Amazon |
| YubiKey 5 NFC | USB-A desktops + NFC phones | Amazon |
| Proton Pass | Passkeys + authenticator-style TOTP | Proton Pass |
We may earn a commission if you buy a YubiKey or sign up for Proton Pass through the links above.
Email authentication (verified DNS)
November 20, 2026 — public DNS only (no numeric audit scoreboards in this article). These facts describe inbound mail identity for the district and vendor domains named in reporting.
| Domain | DMARC | DKIM (public) | Inbound MX |
|---|---|---|---|
| afasd.net | p=quarantine | Present (google selector) | Google Workspace |
| caryspec.com | None (no _dmarc record) | Present (default selector) | SpamExperts fronting Microsoft 365 (spf.protection.outlook.com in SPF) |
Additional checks
| Signal | afasd.net | caryspec.com |
|---|---|---|
| SPF | ~all with _spf.google.com | -all with Outlook include |
| MTA-STS | No _mta-sts TXT | No _mta-sts TXT |
| HTTPS site | Served over TLS (Cloudflare in front) | HTTP 200 on homepage |
Contrast (Workspace provider, not the district): google.com publishes DMARC p=reject and MTA-STS. That does not automatically transfer to afasd.net unless the district enforces aligned SPF/DKIM and upgrades DMARC toward reject.
Readers can run a free scan at audit.emailmenow.com and enter afasd.net or caryspec.com manually.
Illustration only — DNS facts are in the tables above.
Website stack note
Passive website-tech probes on November 20, 2026:
| Domain | Stack signal |
|---|---|
| afasd.net | Stack undetected; jQuery 1.8.0 visible (CVE hint — upgrade path); afasd.net — Let’s Encrypt into Jan 14, 2027; www.afasd.net — Google Trust Services into Jan 28, 2027 |
| caryspec.com | WordPress 7.1.5 (current); PHP 8.4.28 supported; Let’s Encrypt TLS into Jan 11, 2027 |
Point-in-time only. A stale jQuery banner on a district CMS is not evidence of how the August wire was diverted.
Blacklist and lookalike domains
Email blacklist checks (public DoH, November 20, 2026): afasd.net showed UCEPROTECT Level 3 on Google Workspace shared MX — shared-provider noise; do not lead as “the district is blacklisted.” caryspec.com was clear.
Cybersquat scans (BEC profile, registered signals only):
| Brand scanned | To review | BEC staging |
|---|---|---|
| afasd.net | 9 | 0 |
| caryspec.com | 3 | 0 |
Monitoring: Cybersquat Domain Monitoring.
CourtListener
CourtListener REST search on November 20, 2026 found no federal complaint naming this August 2026 payment diversion. Unrelated 2025 dockets (for example Adams Friendship Area School District v. Meta Platforms, Inc.) concern social media, not vendor payment fraud — we do not treat them as signals for this loss.
Related coverage
- Surfside Beach $545K municipal BEC and insurance gaps
- Seventh Circuit denies cyber claim after CFO BEC
- Cyber insurance controls and claims
- Wisconsin school district audit listicle (June 2026)
- MFA support directory
Check your domain free at audit.emailmenow.com, or see automated reports and monitoring.
Sources: WTMJ — Central Wisconsin school district scammed out of $63,000 (Nov 18, 2026) · WDEZ — Adams-Friendship School District Provides Scam Update (Nov 18, 2026) · website-tech, blacklist, cybersquat, and public DNS checks November 20, 2026.