Yes — Baker Tilly Advisory Group, LP reported a cybersecurity incident involving client and dependent data held on a third-party service provider’s platform. Baker Tilly says it learned of the issue on September 6, 2026, finished reviewing affected records on October 28, 2026, and is notifying people by mail and regulatory filings. The vendor is not named in public notices reviewed for this post — we do not speculate on which provider was involved.
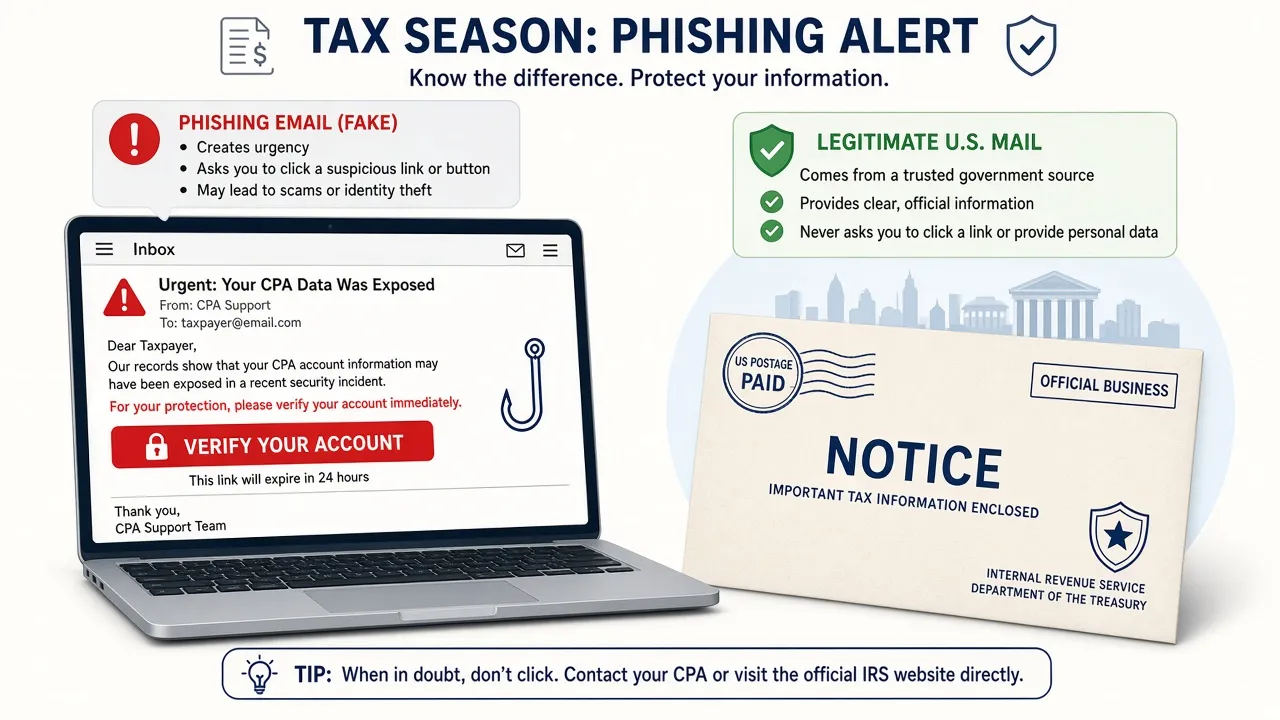
The angle for tax-season security is fourth-party risk: large CPA networks rely on hosted portals, payroll, and document platforms outside their own network. When SSNs leak from a vendor copy, criminals pivot to “your CPA data was exposed — click to enroll” phishing that rides the real notice window.
This post covers confirmed regulatory and trade-press facts, EmailMeNow admin audits (ideal 100%), website-tech, blacklist, lookalike, CourtListener, and YubiKey / Google Authenticator posture on Baker Tilly’s published client-facing login story.
Snapshot
| Field | Detail |
|---|---|
| Organization | Baker Tilly Advisory Group, LP (bakertilly.com) |
| Incident surface | Third-party platform — vendor not named publicly |
| Baker Tilly awareness | September 6, 2026 (BleepingComputer) |
| Review completed | October 28, 2026 (same) |
| Breach date (CA AG sample) | September 2, 2026 (California AG SB 24-632686) |
| Texans affected (OAG) | 10,456 — published November 10, 2026 |
| Texas data types (OAG) | Name, address, Social Security number, other |
| Notice method (Texas OAG) | U.S. Mail |
| Monitoring offered | 24 months credit and identity monitoring via Experian (per BleepingComputer citing customer notice) |
| Ransomware claims | None located at publish time (BleepingComputer) |
What Baker Tilly and regulators say
Per BleepingComputer (November 11, 2026), citing Baker Tilly’s customer notification:
- An unauthorized actor obtained data relating to certain Baker Tilly clients from a platform operated by a third-party service provider.
- Baker Tilly took containment steps, engaged external investigators, and notified law enforcement.
- The firm says it has no evidence of unauthorized activity on its own network and no reports of identity theft or fraud tied to the exposure at the time of the notice.
- The customer letter reviewed by BleepingComputer left some data-type fields as placeholders; Texas and California AG filings carry more structured fields.
The California Attorney General sample notice lists Baker Tilly Advisory Group, LP with breach date September 2, 2026 and publication November 9, 2026.
Repository Texas OAG structured data (synced with the public portal) lists Baker Tilly at 311 N Green St, Suite 600, Chicago, IL, with 10,456 Texans affected and data types name, address, Social Security number, and other. That record published November 10, 2026 with consumer notice Yes via U.S. Mail.
Baker Tilly is a large U.S. accounting and advisory network (audit, tax, consulting). Global footprint and revenue figures in trade press (147 countries, $6.8 billion revenue) come from BleepingComputer’s article — treat them as secondary context, not a substitute for Baker Tilly’s own annual report if you need investment-grade figures.
Who may be in scope
| Group | Detail |
|---|---|
| Baker Tilly clients | People the firm serves on tax, audit, or advisory engagements |
| Dependents | Notification text references client and dependent personal information |
| Multi-state residents | Texas count is published; other states may file separately |
Data types confirmed in public filings
| Source | Fields named |
|---|---|
| Texas OAG | Name, address, SSN, other |
| Customer notice (via BleepingComputer) | Personal information about clients and dependents; some notice fields still generic |
| California AG sample | Breach date 09/02/2026; entity name only in the public sample page |
Do not treat dark-web counts or leak-site posts as confirmed unless Baker Tilly or a regulator publishes them. BleepingComputer reported no ransomware gang claim at publish time.
Why CPA firms should treat vendor copies as breach surface
Accounting firms are data brokers in practice: returns, K-1s, payroll, and dependent SSNs often sit on vendor SaaS, not only on the firm’s LAN. IRS Publication 4557 and the FTC Safeguards Rule still require a written information security plan that covers service providers — selection, contract terms, and oversight.
When a vendor platform leaks:
- W-2 and 1099 fraud timing worsens heading into January–April filing season.
- Lookalike domains can spoof “Experian activation” or “secure document upload” while the real firm mails paper notices.
- Transport gaps on the firm’s own domain still matter: even a perfect vendor contract does not stop
@bakertilly.comspoof if DMARC and MTA-STS are weak.
See the national CPA firm audit scorecard for how large networks cluster on transport scores.
Independent domain audits (admin API)
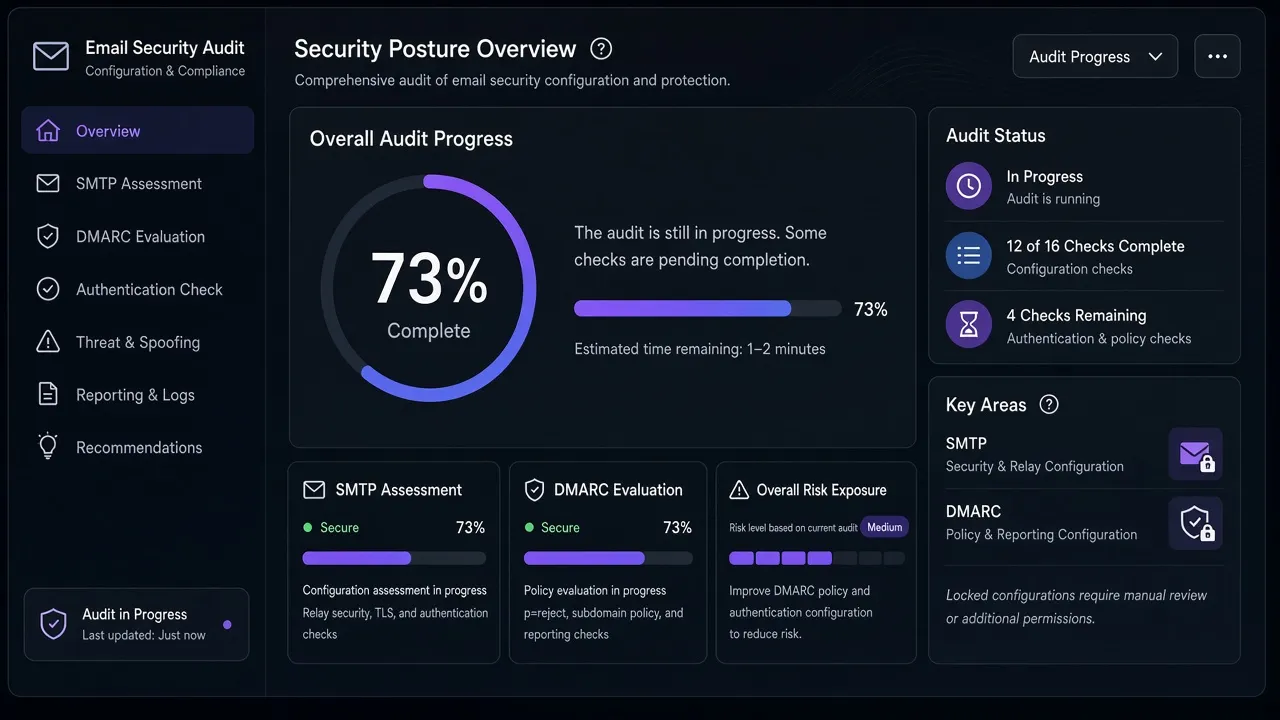
We ran EmailMeNow admin scans on November 17, 2026 via GET https://audit.emailmenow.com/api/admin/scan (not the public ?domain= form). 100% is the ideal overall domain-security score. 0 of 2 in-scope hosts reach it.
| Organization | Domain | Overall | Gap vs 100% |
|---|---|---|---|
| Baker Tilly | bakertilly.com | 73% | −27 |
| Experian (monitoring vendor) | experian.com | 66% | −34 |
| Domain | Identity | Transport | Website |
|---|---|---|---|
| bakertilly.com | 65% | 15% | 90% |
| experian.com | 50% | 15% | 90% |
How to read this: These scores measure public email authentication, transport policy, and website headers on each primary domain. They do not prove or disprove the unnamed third-party breach. They do predict how convincingly an attacker can send fake breach follow-up mail that appears to originate from the firm or monitoring vendor during a real notice window.
The 15% transport score on both hosts is the familiar MTA-STS enforcement gap seen across large professional-services domains. A 73% overall on bakertilly.com is above the 60% snapshot in our June 2026 national CPA listicle — this post uses the November 17 admin pass only.
Re-run any domain at audit.emailmenow.com (search the domain on the homepage — no bookmarked ?domain= links required).
Website stack note
Passive website-tech probe on November 17, 2026:
| Domain | Stack signal |
|---|---|
| bakertilly.com | Next.js; X-Powered-By exposes stack detail |
| experian.com | (not re-probed this pass — monitoring enrollment uses Experian’s consumer domains) |
TLS on bakertilly.com: Let’s Encrypt, valid per Certificate Transparency with expiry into January 2027 at probe time. Point-in-time only — stack fingerprint is not evidence about the unnamed vendor incident.
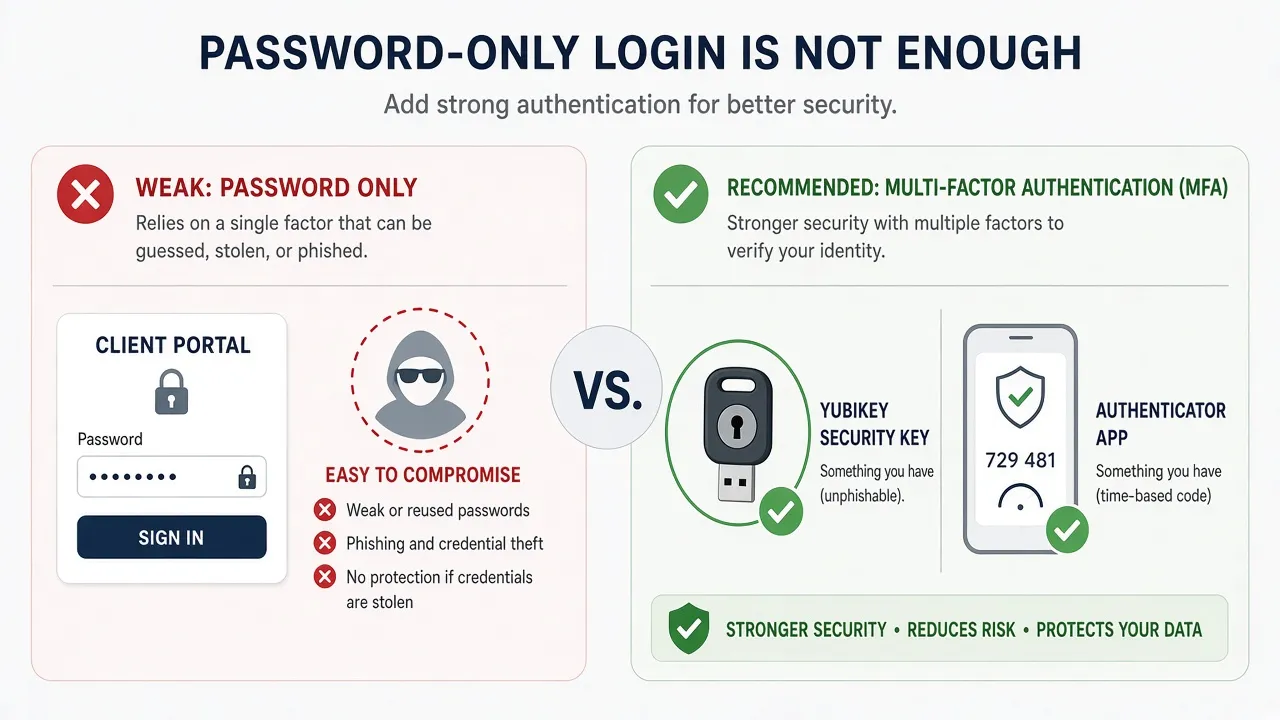
MFA: US client portal is username/password — no published YubiKey or Google Authenticator path
Baker Tilly’s published Client Portal Agreement states the portal is provided through Thomson Reuters and access requires a username and password. The agreement describes username/password as “an adequate form of security” and does not document YubiKey, FIDO, or Google Authenticator / open TOTP for US clients.
| Method | Documented for US Baker Tilly client portal? | Grade impact |
|---|---|---|
| Username + password | Yes (Thomson Reuters portal) | Fail (single factor) |
| YubiKey / FIDO2 | Not documented | No Strong path |
| Google Authenticator / open TOTP | Not documented | No Pass path |
| Passkeys | Not documented | No Partial promote |
Baker Tilly publishes IAM guidance for clients’ own programs (identity and access management insight) — that is advisory content, not a description of MFA on the US client portal you use to exchange tax documents.
Workforce Microsoft 365 accounts may use organization-enforced MFA (Microsoft support) — that is tenant policy, not something this post attributes to Baker Tilly without a public workforce standard.
Experian breach monitoring enrollment will have its own consumer login. Victims should activate monitoring through the Experian letter or URL Baker Tilly mailed, not through search ads or SMS links.
How we grade: Fail = password-only or SMS/phone as the documented consumer path; Pass = open TOTP; Strong = FIDO/YubiKey. Same rules as the MFA directory.
Recommended MFA tools (for your firm and personal mail)
Use these on systems that document them — not on the Baker Tilly client portal above, which does not.
| Product | Best for | Get it |
|---|---|---|
| YubiKey 5C NFC | USB-C laptops + NFC phones | Amazon |
| YubiKey 5 NFC | USB-A desktops + NFC phones | Amazon |
| Proton Pass | TOTP vault + passkeys where supported | Proton Pass |
We may earn a commission if you buy through the links above.
Blacklist, lookalikes, CourtListener
Email blacklist (public DoH, November 17, 2026): bakertilly.com — clear (no mail/domain listings on checked DNSBLs). SPFBL notes on web/CDN IPs are low-signal provider noise — do not lead news copy on them.
DNS lookalike scan (bakertilly.com, standard profile, November 17, 2026):
| Metric | Count |
|---|---|
| Lookalikes to review | 22 |
| Likely Baker Tilly–owned redirects | 3 (bakertilly.io, .net, .us) |
| BEC staging (MX) | 4 |
| Lookalike | Technique | Note |
|---|---|---|
| baker-tilly.com | Hyphenation | BEC staging (MX) |
| bakerilly.com | Omission | BEC staging (MX) |
| bakertilly.cloud | TLD swap | BEC staging (MX) |
| bakertlily.com | Transposition | BEC staging (MX) |
| baketilly.com | Omission | Registered — typo-domain lure risk |
Type bakertilly.com yourself for any portal or careers link. During a breach notice, hyphenation and omission domains are high-value lures for “dependent SSN verification” forms.
CourtListener
| Court | Result |
|---|---|
| Texas federal (TXSD / TXED / TXND / TXWD) | 0 RECAP hits on "Baker Tilly" data breach at re-check |
| S.D.N.Y. | Stassi v. Baker Tilly Advisory Group, LP, 1:26-cv-09911, filed November 12, 2026 — diversity contract caption (docket) |
The New York filing arrived in the same calendar window as AG publications. We did not read the complaint; it is not labeled a data-breach class action in the public index. Treat it as an early litigation signal, not as proof of additional facts beyond regulatory notices.
What clients and firms should do
If you received Baker Tilly’s letter:
- Use the Experian activation steps in the mailed notice — not links from unexpected email or SMS claiming “your SSN was leaked.”
- Place a credit freeze at Equifax, Experian, and TransUnion. Free monitoring helps after exposure; a freeze blocks new account openings.
- Watch for 1099 and W-2 phishing that references Baker Tilly or “your CPA firm breach.”
- Flag dependent SSN exposure — children’s credit files are frequent fraud targets after family-tax data leaks.
If you run a CPA or tax firm:
- Inventory every vendor that stores SSNs or bank data — including portals, OCR, and hosted QuickBooks / payroll pipes.
- Require DMARC
p=reject, MTA-STS enforce, and phishing-resistant MFA on firm mail and client upload paths that you control. - Run a domain audit at audit.emailmenow.com and review automated monitoring options.
Related reading
- National CPA firm email security audit
- Texas CPA firm OAG breach tracker
- Texas OAG YTD dashboard
- MFA directory — YubiKey, TOTP, passkeys
- CFGi ShinyHunters breach (accounting-sector precedent)
- Cybersquat Domain Monitoring
Sources: California AG SB 24-632686 · BleepingComputer Nov 11, 2026 · Texas OAG breach portal · Texas OAG structured export in this repo (data/texas-oag-breach-reports.json) · Baker Tilly Client Portal Agreement · Baker Tilly client portal overview · Microsoft 365 MFA setup (workforce context) · EmailMeNow admin audits November 17, 2026 · website-tech, blacklist, and cybersquat probes November 17, 2026 · CourtListener November 17, 2026
Check your domain free at audit.emailmenow.com, or see automated reports and monitoring.