The FBI issued an urgent public service announcement about Kali365, a phishing-as-a-service (PhaaS) platform that lets attackers steal Microsoft 365 OAuth tokens and gain persistent access without passwords or additional MFA challenges — even when victims have multi-factor authentication enabled.
Read the FBI IC3 PSA:
https://www.ic3.gov/PSA/2026/PSA260521
What Is Kali365
First observed in April 2026, Kali365 is distributed primarily via Telegram. Subscribers get AI-generated lures, automated campaign templates, victim-tracking dashboards, and device-code OAuth capture — lowering the skill bar for compromising Microsoft 365 tenants.
The FBI warns the kit enables access to Outlook, Teams, OneDrive, and other SSO-connected SaaS apps, fueling data theft, BEC wire fraud, and ransomware follow-on activity.
How the Attack Works
- Lure — Victim receives email impersonating a trusted cloud or document-sharing service with a device code and instructions to visit Microsoft’s real verification page.
- Authorization — Victim pastes the code on login.microsoftonline.com, unknowingly authorizing the attacker’s application.
- Token theft — Attacker captures OAuth access and refresh tokens.
- Persistence — Attacker uses the tokens repeatedly without re-entering MFA.
This is device-code phishing — it abuses Microsoft’s legitimate OAuth 2.0 device authorization flow rather than stealing passwords.
Illustrated attack chain
Step 1: Phishing lure with a device code
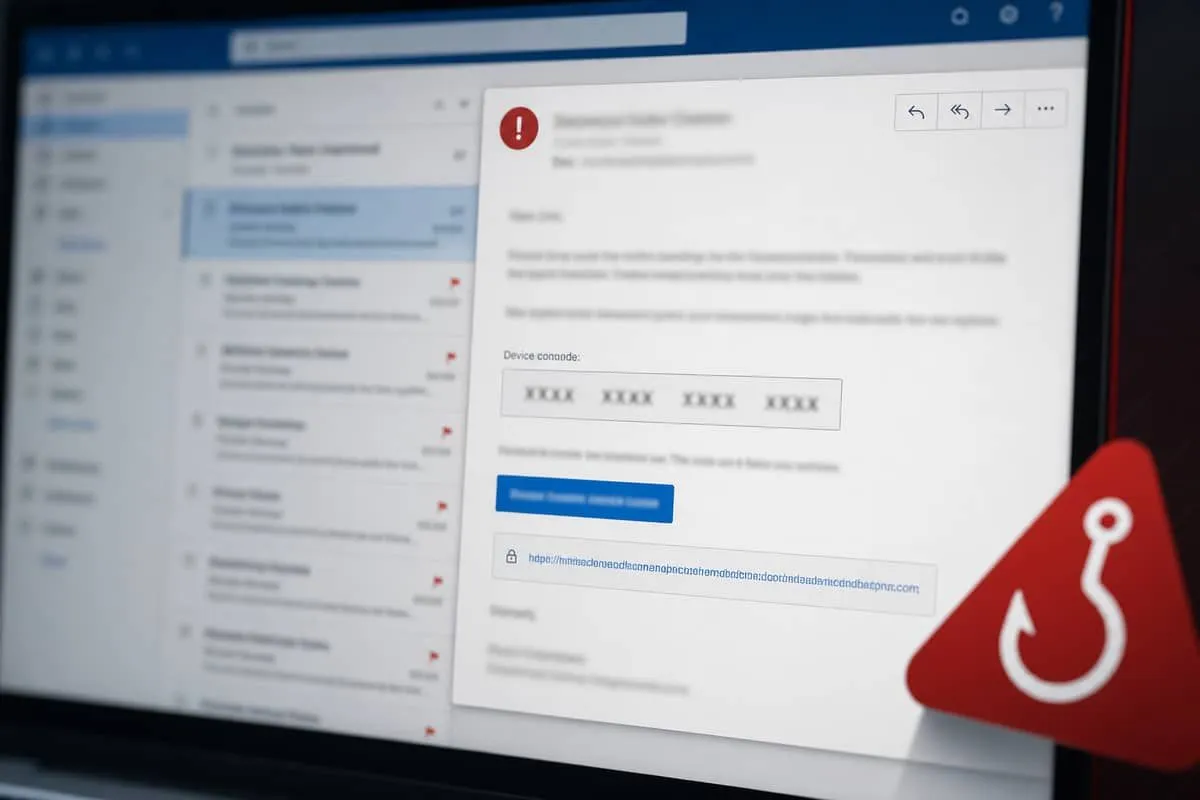
The victim receives email impersonating a trusted cloud or document service with a device code and instructions to visit Microsoft’s real verification page.
Step 2: Victim authorizes on the real Microsoft login page
The victim pastes the code on login.microsoftonline.com, unknowingly authorizing the attacker’s application — a legitimate Microsoft page, not a fake clone.
Step 3: Attacker captures OAuth tokens
The attacker captures OAuth access and refresh tokens and reuses them without re-entering MFA — persistent access to Outlook, Teams, OneDrive, and SSO-connected SaaS apps.
FBI and Defender Recommendations
- Create Conditional Access policies to block or restrict device code flow for all users except documented exceptions.
- Block authentication transfer policies that let sessions move between devices.
- Audit sign-in logs for device-code grants and unfamiliar application consents.
- Revoke sessions (
revokeSignInSessions) for compromised accounts immediately. - Watch for mailbox rules, new device registrations, and OAuth app consents after incidents.
- Report victims to IC3.gov.
Kali365 joins EvilTokens, Tycoon2FA, and other 2026 PhaaS platforms using the same technique. For a state-sponsored chain that turns stolen directories into trusted-contact phishing and MFA device registration, see our COLD RELIC breakdown.
Why Texas Law Firms and RIAs Are Targets
Legal and financial firms are heavy Microsoft 365 users with high-value mailboxes and wire-transfer workflows. A single compromised partner or paralegal account can expose client privilege, trust accounting, and SEC/FTC-regulated customer data.
This threat pairs with the April 2026 wave of vishing and SaaS attacks we summarized in our April cyber incidents roundup — identity-layer attacks that bypass traditional perimeter controls.
Independent Cybersecurity Audit
We audited Microsoft’s primary domains on June 22, 2026:
| Organization (Domain) | Overall | Risk Level |
|---|---|---|
| Microsoft (microsoft.com) | 73% | Good |
| Microsoft 365 / Office (office.com) | 59% | High Risk |
Strong microsoft.com scores do not stop Kali365 — victims authorize real Microsoft pages. The office.com gap in the High Risk band is a reminder that impersonation of Microsoft login flows remains effective when staff are not trained on device-code scams.
Audit links:
Harden Microsoft 365 before attackers do.
Check your domain free at audit.emailmenow.com or see automated reports and monitoring.
Related trackers
- Texas OAG YTD dashboard
- Healthcare AG breach tracker
- Law firm breach tracker
- Financial services tracker
- Monitoring guide
- Washington healthcare breaches (2026)
- Washington law firm breaches (2026)
- CA November roundup
- TX November roundup
- WA September roundup
- TX Parks breach
- Have I Been Pwned
- HIBP October roundup
- Breach data week (November)
- HHS OCR October roundup
- SEC 8-K October roundup
- All trackers
Sources: FBI IC3 — Kali365 PSA · EmailMeNow audits — microsoft.com · office.com